Book a scoping callBook a call

One request from someone else's data

The whole application, tested by hand: authentication, access control, input handling and business logic, and what an attacker reaches through them.

During the test

See progress and confirmed findings as they are reported

As the test progresses, the checklist is updated and each confirmed finding is added to Outer Core with evidence, impact and remediation guidance. Your team can follow the engagement, ask questions and start fixing issues before the final report is ready.

Checklist progress across the agreed test areas
Evidence and demonstrated impact on each finding
Questions and remediation kept with the finding
What we look for

The attacker's hit list

A representative sample of the dozens of checks we run against the OWASP ASVS, spanning authentication, access control, injection, business logic, and client-side.

Broken authentication and session handling

weak password-reset and recovery flows, sessions that outlive logout, one-time codes you can replay.

Access-control gaps: IDOR and privilege escalation

objects you can reach by editing an ID in the request, actions one role can run as another.

Injection: SQL, template, command and beyond

unsanitized input reaching a database query, a template engine, or the shell.

Business-logic abuse unique to your app

coupons, quotas, and multi-step flows driven out of the order they were meant to run.

Client-side issues: XSS, CSRF, DOM sinks

user input echoed straight into the page, state-changing requests with no anti-forgery check.

5 checks
Broken authentication and session handling

weak password-reset and recovery flows, sessions that outlive logout, one-time codes you can replay.

Access-control gaps: IDOR and privilege escalation

objects you can reach by editing an ID in the request, actions one role can run as another.

Injection: SQL, template, command and beyond

unsanitized input reaching a database query, a template engine, or the shell.

Business-logic abuse unique to your app

coupons, quotas, and multi-step flows driven out of the order they were meant to run.

Client-side issues: XSS, CSRF, DOM sinks

user input echoed straight into the page, state-changing requests with no anti-forgery check.

How we test

A full application pentest, from attack surface to confirmed impact

01

Map the attack surface

We map the architecture, roles, workflows, endpoints, inputs, integrations and trust boundaries across the application.

02

Test every layer

We test authentication and sessions, access control, input handling and injection, browser security, configuration and business logic.

03

Validate and connect findings

We reproduce each weakness, confirm its impact, follow useful connections between findings and document the evidence your team needs.

What you get

A report your team can work from

A single reviewed report your engineers and your auditors can both act on.
Penetration Test Report
acme-app / web / engagement summary
01Findings ranked by real impactSeverity reflects the data or action each issue exposes and how hard it is to reach.
02Reproduction steps for every issueThe exact steps to trigger each finding, replayable by your team first try.
03Fix guidance your developers can act onThe concrete change and where it belongs in the framework you run.
04Free retesting for one yearAfter you remediate a finding, we rerun the original proof in the tested context and record the result.
The actual report, page by page
Watermarked sample report page: The report your team receives
01The report your team receives
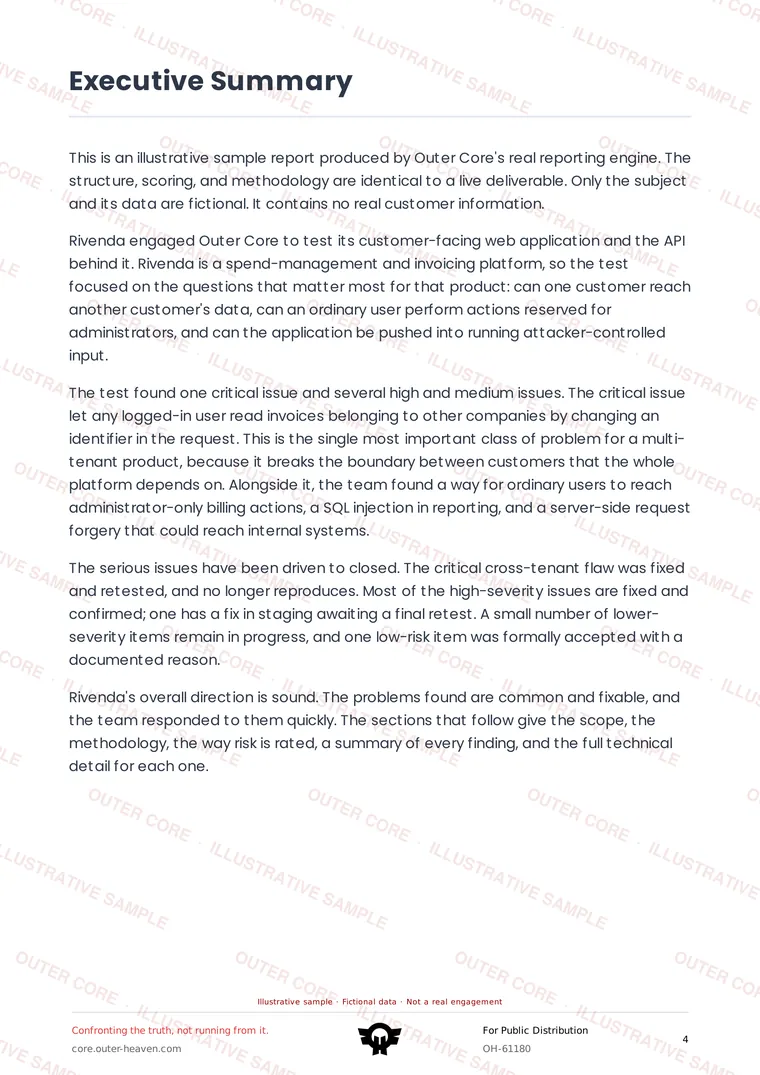
Watermarked sample report page: Executive summary
02Executive summary
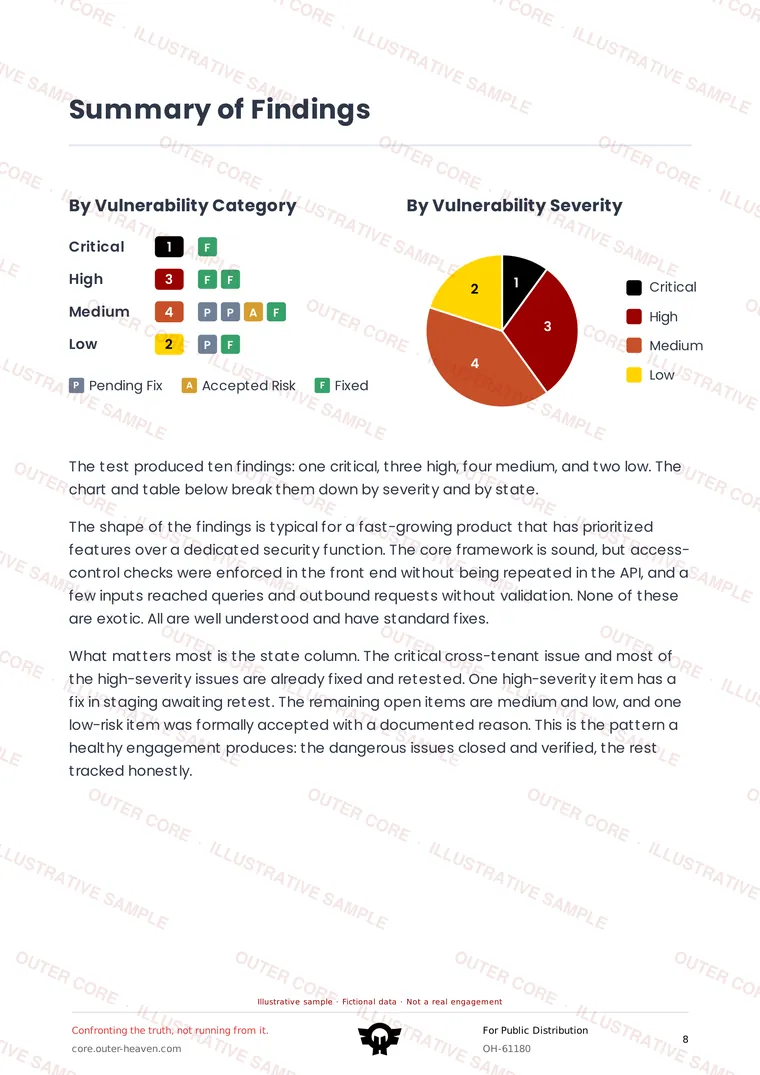
Watermarked sample report page: Findings, ranked by impact
03Findings, ranked by impact
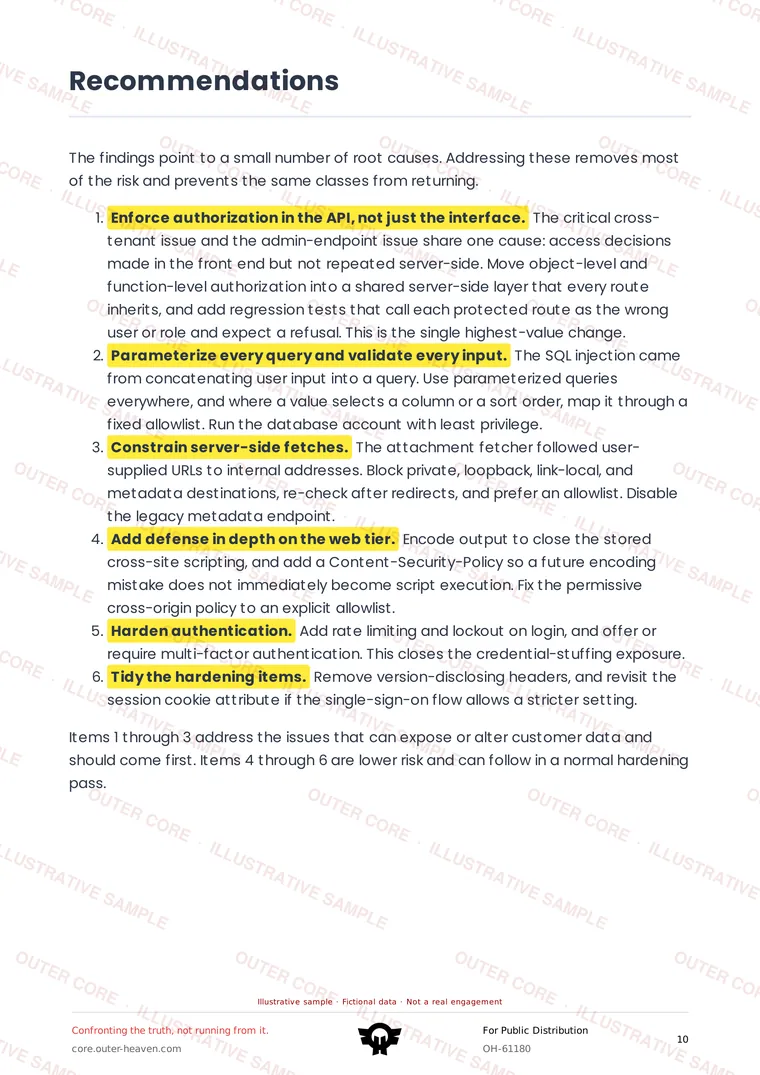
Watermarked sample report page: Recommendations
04Recommendations
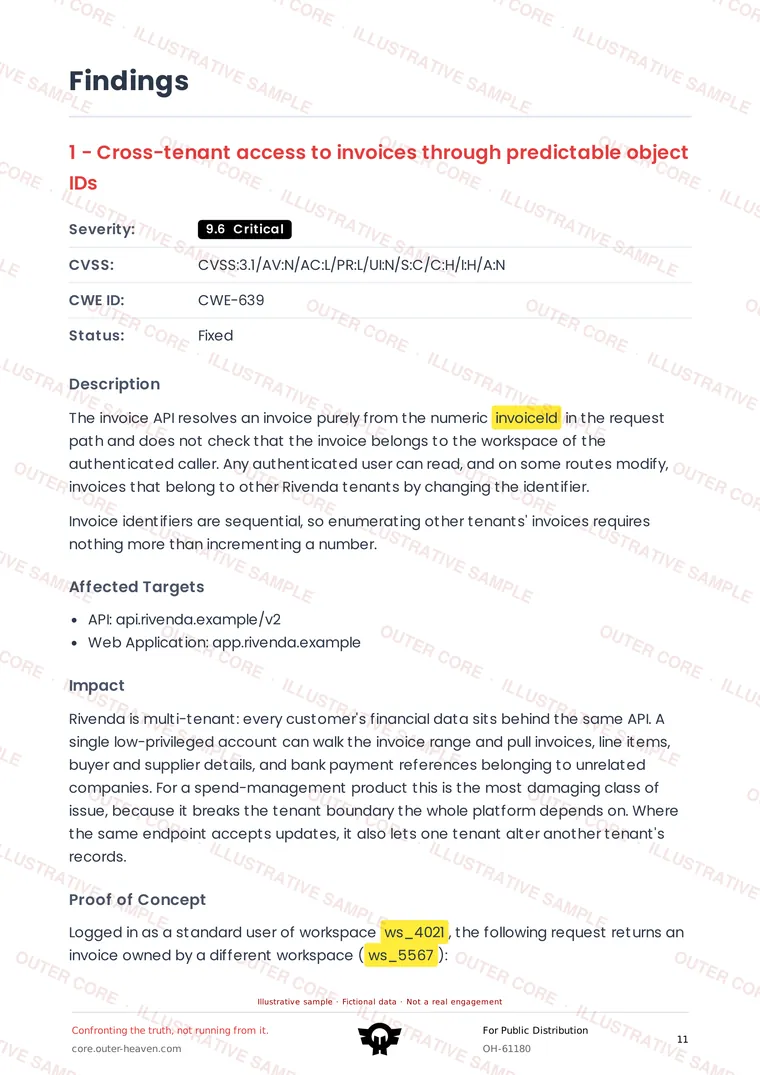
Watermarked sample report page: A finding, reproduced in full
05A finding, reproduced in full
5 sample pages

You're seeing 5 pages. The full report is the complete PDF a customer receives.

As the tester completes the checklist, confirmed findings appear in Outer Core with evidence and remediation guidance. You can ask questions on the finding, send it to GitHub and request a retest after the fix.

See how delivery works
Get started

See your web app the way an attacker will

Book a scoping call and we'll define the targets, roles, depth and testing window together. Confirmed findings will appear in Outer Core while the engagement is running.

Book a scoping call