Book a scoping callBook a call

One wildcard from account admin

AWS, Azure and GCP: over-permissive IAM, exposed storage and the trust relationships that let a single leaked key become the whole account.

The escalation path

We read the policy the way an attacker does

A benchmark tool flags a checkbox. We follow the grant. One over-broad statement rarely stops at the resource it names. It's a hop toward everything that role can reach.

Wildcards in Action and Resource, traced to reach
Trust policies that let one role become another
The full path from foothold to account owner
iam / role/s3-reader / policy.json
1{
2 "Effect": "Allow",
3 "Action": "*",
4 "Resource": "*",
5 "Principal": {
6 "AWS": "arn:aws:iam::…:role/s3-reader"
7 }
8}
CriticalAction + Resource wildcards → this role can rewrite its own permissions.
privilege-escalation path
01
Public bucket

A misconfigured S3 bucket leaks a backup with credentials.

02
Leaked key

The access key belongs to the over-permissioned s3-reader role.

03
sts:AssumeRole

The wildcard lets the role assume a far more privileged one.

04
Account adminCritical

From there, full control of the account and everything in it.

01
Public bucket

A misconfigured S3 bucket leaks a backup with credentials.

02
Leaked key

The access key belongs to the over-permissioned s3-reader role.

03
sts:AssumeRole

The wildcard lets the role assume a far more privileged one.

04
Account admin

From there, full control of the account and everything in it.

What we look for

Where the account gives

A representative sample of the dozens of checks we run against the CIS Benchmarks, spanning identity, storage, compute, networking, and secrets across your cloud accounts.

Over-permissive IAM roles and policies

wildcard permissions, and roles that can quietly grant themselves more.

Publicly exposed storage, snapshots and images

buckets, disk snapshots, and machine images reachable from the open internet.

Privilege escalation through role assumption

one role allowed to assume another, chained until it reaches admin.

Misconfigured network and security groups

subnets and security groups left open to the whole internet on ports that should not face out.

Secrets in metadata, functions and pipelines

keys sitting in instance metadata, function environment variables, and CI logs.

5 checks
Over-permissive IAM roles and policies

wildcard permissions, and roles that can quietly grant themselves more.

Publicly exposed storage, snapshots and images

buckets, disk snapshots, and machine images reachable from the open internet.

Privilege escalation through role assumption

one role allowed to assume another, chained until it reaches admin.

Misconfigured network and security groups

subnets and security groups left open to the whole internet on ports that should not face out.

Secrets in metadata, functions and pipelines

keys sitting in instance metadata, function environment variables, and CI logs.

How we test

Inventory identities, analyse permissions and confirm escalation

Step 01

Inventory the account

Identities, resources and the trust relationships between them, across AWS, Azure and GCP.

Step 02

Analyse privilege paths

We map who can become whom, and where a wildcard quietly widens reach.

Step 03

Prove escalation

From a realistic foothold, we demonstrate the walk to account takeover.

What you get

Configuration findings mapped to the resulting access path

Each misconfiguration comes with the policy change that closes the path to your data.
Penetration Test Report
acme-app / cloud / engagement summary
01Misconfigurations mapped to benchmarksFindings reference relevant CIS and provider guidance and explain the demonstrated impact.
02The privilege-escalation paths that matterThe chains that reach your data or the account owner.
03Remediation as concrete policy changesThe exact statement to tighten, in your provider and IaC.
04Free retesting for one yearAfter you remediate a finding, we rerun the original proof in the tested context and record the result.
The actual report, page by page
Watermarked sample report page: The report your team receives
01The report your team receives
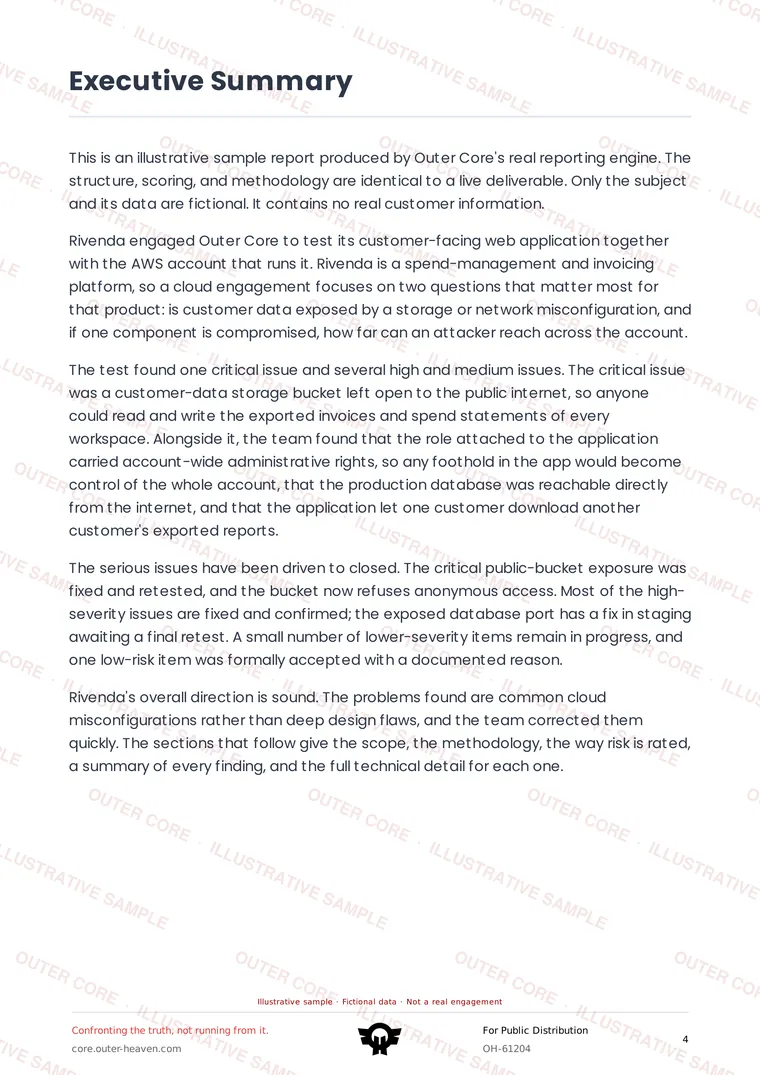
Watermarked sample report page: Executive summary
02Executive summary
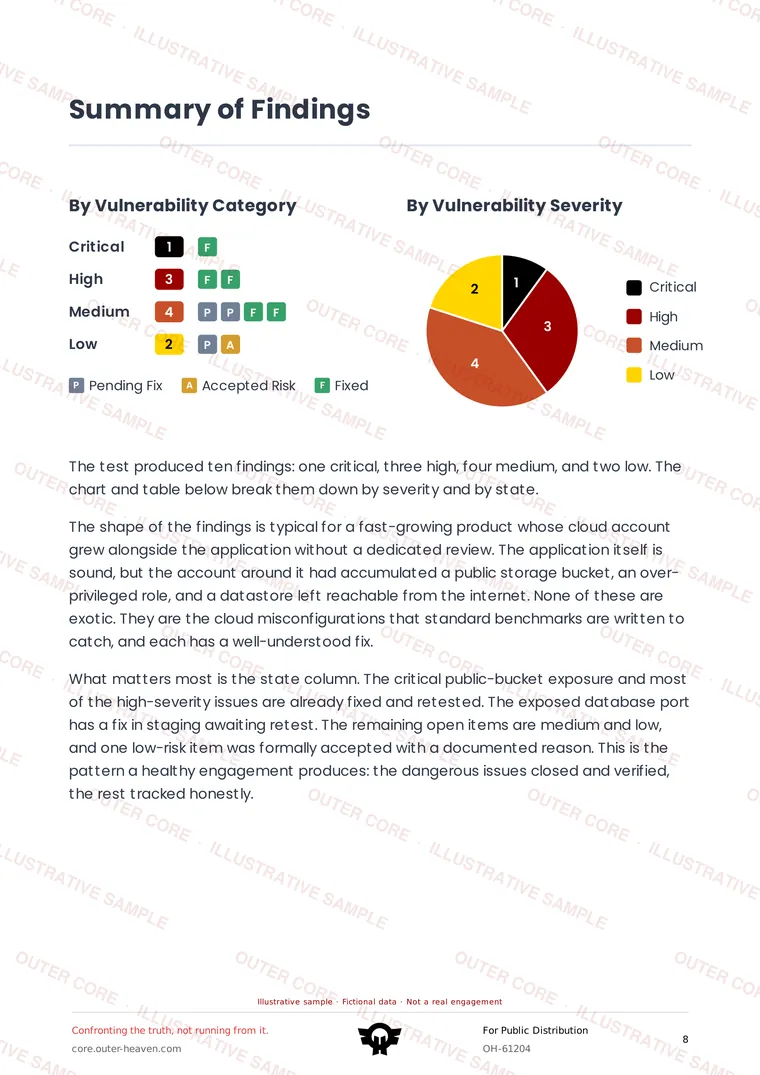
Watermarked sample report page: Findings, ranked by impact
03Findings, ranked by impact
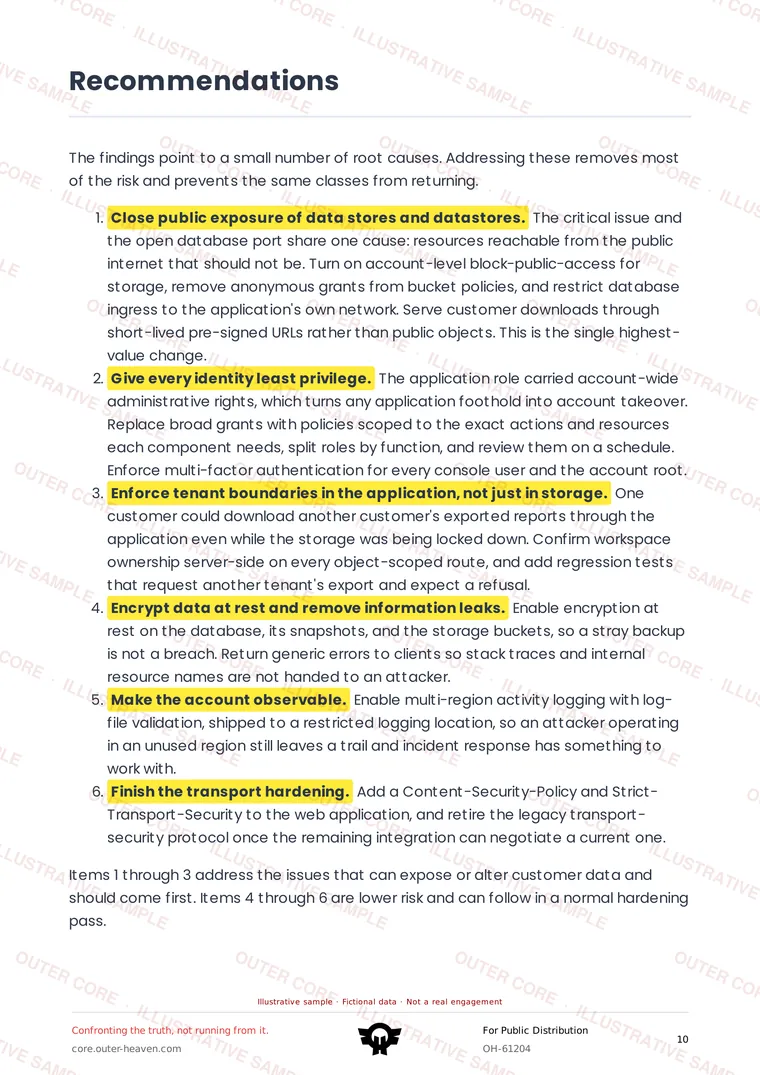
Watermarked sample report page: Recommendations
04Recommendations
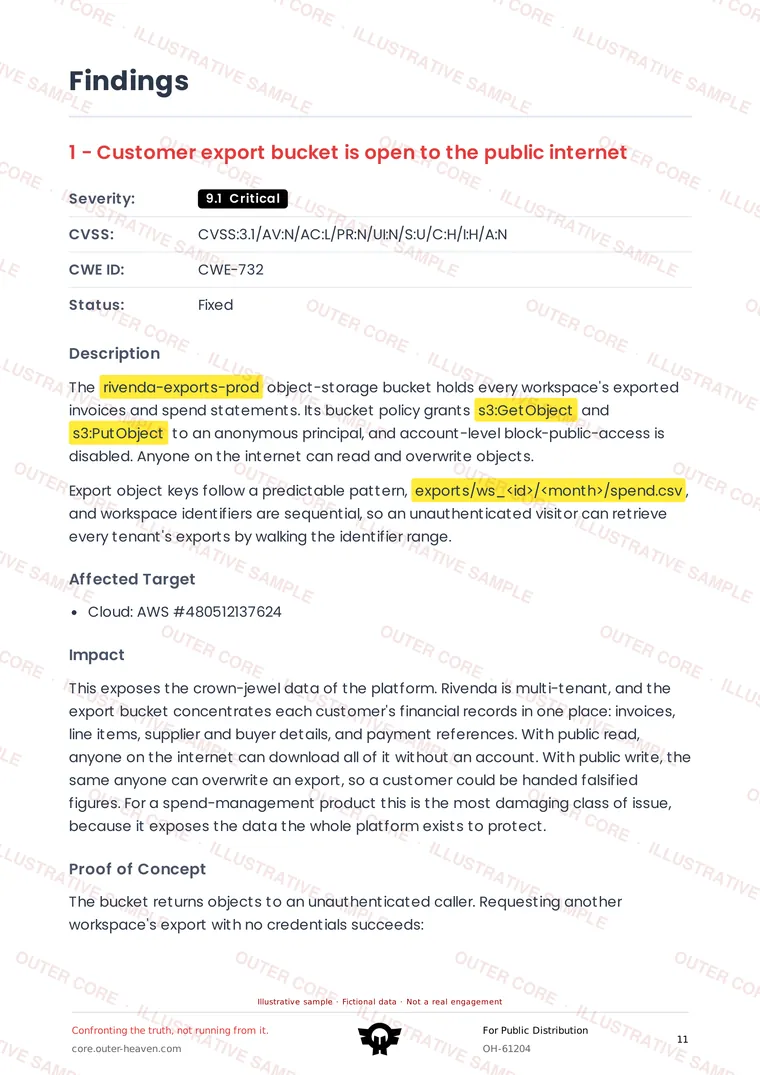
Watermarked sample report page: A finding, reproduced in full
05A finding, reproduced in full
5 sample pages

You're seeing 5 pages. The full report is the complete PDF a customer receives.

Confirmed cloud findings appear with the affected identity, policy statement, evidence and resulting access. Your team can discuss the policy change, send the work to GitHub and request a retest.

See how delivery works
Get started

Close the path before it reaches the root account

Book a scoping call and we'll define the accounts, providers, access and testing depth together. Confirmed findings and escalation paths will appear in Outer Core during the engagement.

Book a scoping call