Book a scoping callBook a call

The app ships with its secrets inside

Android and iOS, against OWASP MASVS. We decompile the binary, instrument it at runtime, and attack the backend it quietly trusts.

Inside the app

What the app carries, we pull out

Anything shipped in the package is readable by anyone who installs it. We decompile, unpack and instrument, surfacing the keys, tokens and shortcuts developers assumed no one would look for.

Static analysis of the decompiled binary
Runtime instrumentation and traffic interception
The backend API the app trusts, tested too
com.acme.app v4.2 (release)
AndroidManifest.xmlMEDIUM
Debuggable flag left enabled
android:debuggable="true"
res/strings.xmlCRITICAL
Hardcoded API key in the package
API_KEY = "sk_live_9f2a…c31"
network_security_configHIGH
Certificate pinning disabled
trustAll = true
SharedPreferencesHIGH
Session token in plaintext storage
lib/*.soread, nothing exposed
Info.plistMEDIUM
Debuggable build entitlement
get-task-allow = true
app bundleCRITICAL
Hardcoded API key in the bundle
API_KEY = "sk_live_9f2a…c31"
Info.plist / ATSHIGH
App Transport Security disabled
NSAllowsArbitraryLoads = true
NSUserDefaultsHIGH
Session token stored outside the Keychain
Frameworks/read, nothing exposed
Trust boundary
backend APIoff device, also in scope
POST /v1/auth
Authorization: Bearer …
What we look for

Where the app leaks

A representative sample of the dozens of checks we run against the OWASP MASVS / MASTG, spanning local storage, cryptography, network security, platform interaction, and tamper resistance.

Hardcoded secrets and API keys in the binary

keys, tokens, and endpoints you can pull straight out of the app package.

Insecure local data storage

session tokens and personal data cached in the clear on the device.

Missing certificate pinning: MITM exposure

traffic a proxy on the same network can read and rewrite.

Broken auth between the app and its backend

trust the client should not hold, checks the server should repeat and does not.

Weak reverse-engineering and tampering resistance

an app that is trivial to unpack, patch, and repackage.

5 checks
Hardcoded secrets and API keys in the binary

keys, tokens, and endpoints you can pull straight out of the app package.

Insecure local data storage

session tokens and personal data cached in the clear on the device.

Missing certificate pinning: MITM exposure

traffic a proxy on the same network can read and rewrite.

Broken auth between the app and its backend

trust the client should not hold, checks the server should repeat and does not.

Weak reverse-engineering and tampering resistance

an app that is trivial to unpack, patch, and repackage.

How we test

Inspect the package, observe it at runtime and test the backend

Step 01

Static analysis

We decompile and read the binary: secrets, endpoints and logic hidden in the package.

Step 02

Dynamic analysis

We instrument the running app and intercept its traffic to break trust at runtime.

Step 03

Attack the backend

The API the app relies on is tested the same way an attacker would, without the app.

What you get

Findings across the application and its backend

One report your iOS and Android teams can both act on.
Penetration Test Report
acme-app / mobile / engagement summary
01Findings across app and backendBoth sides of the boundary: the binary and its API.
02Reproduction with the exact toolingThe decompiler, proxy and instrumentation to reproduce it.
03Fix guidance for iOS and AndroidPlatform-specific remediation, mapped to OWASP MASVS controls.
04Free retesting for one yearAfter you remediate a finding, we rebuild against the agreed binary and record whether the original proof still works.
The actual report, page by page
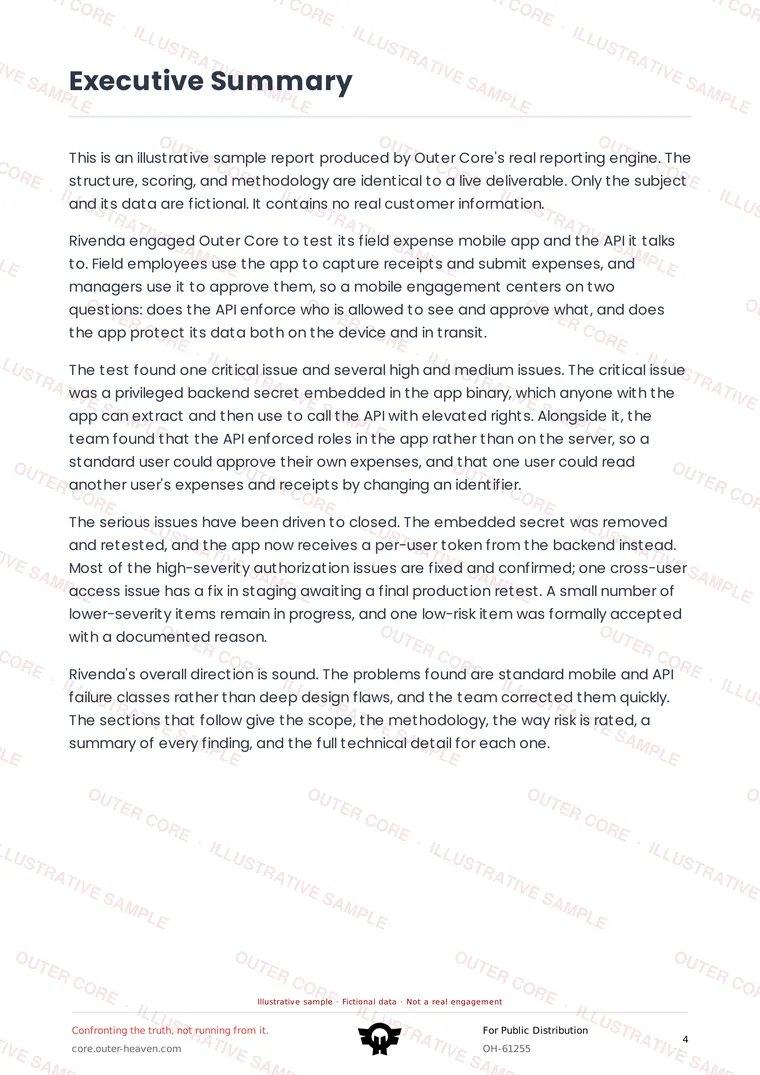
Watermarked sample report page: The report your team receives
01The report your team receives
Watermarked sample report page: Executive summary
02Executive summary
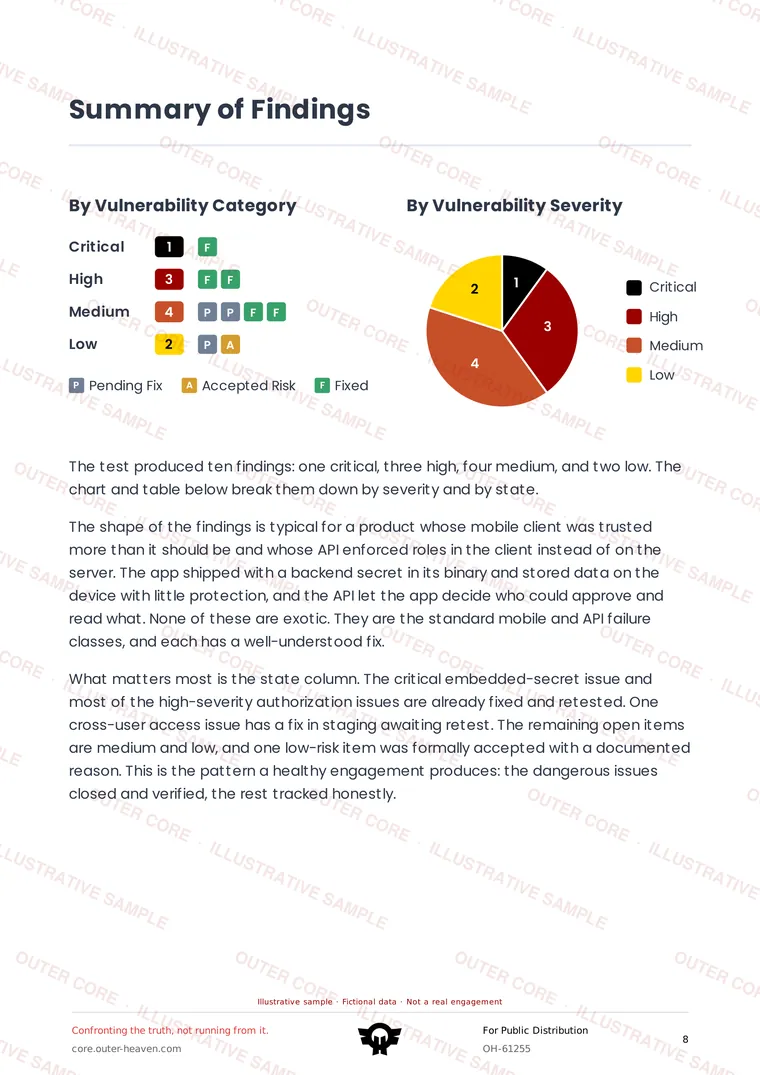
Watermarked sample report page: Findings, ranked by impact
03Findings, ranked by impact
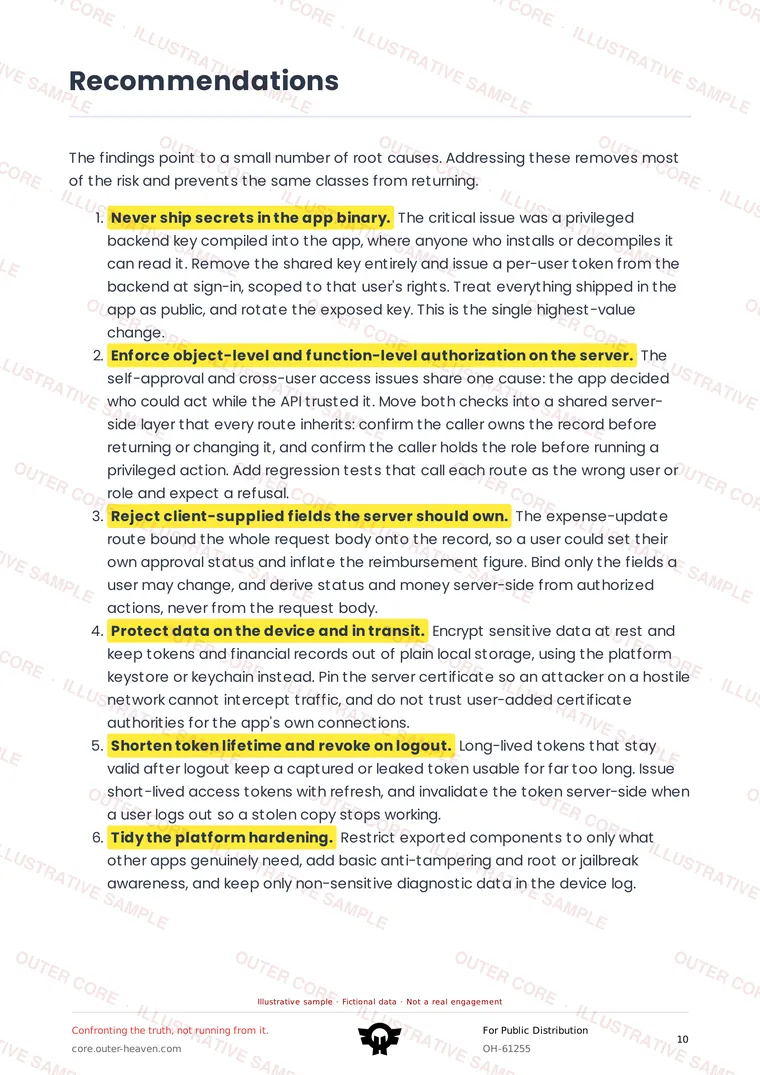
Watermarked sample report page: Recommendations
04Recommendations
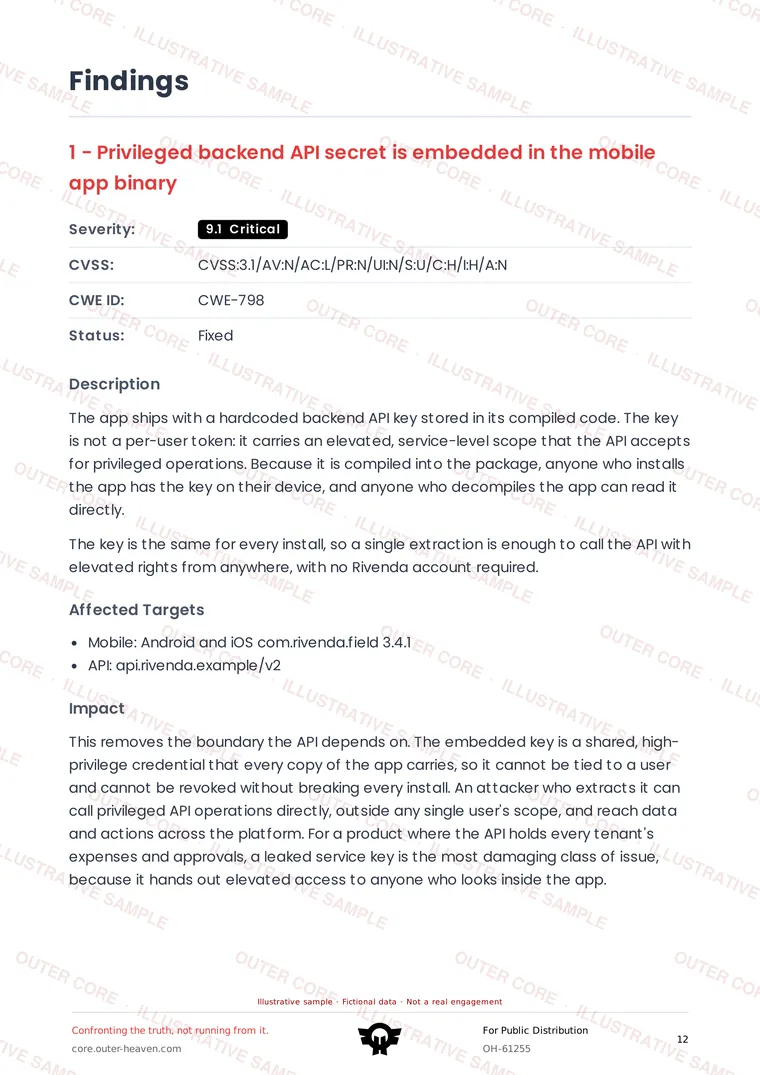
Watermarked sample report page: A finding, reproduced in full
05A finding, reproduced in full
5 sample pages

You're seeing 5 pages. The full report is the complete PDF a customer receives.

Confirmed mobile findings appear with the location in the package or captured traffic, the demonstrated impact and steps your engineers can reproduce. The same record carries remediation and retest results.

See how delivery works
Get started

See what ships in your app before your users do

Book a scoping call and we'll define the platforms, builds, backend access and testing depth together. Confirmed findings will appear in Outer Core during the engagement.

Book a scoping call