Book a scoping callBook a call

From one foothold to domain admin

External perimeter and internal lateral movement: exposed services, misconfigurations, and the path from a single weak point to the whole directory.

The attack path

See how one foothold leads to the next

A forgotten perimeter service can become the first step in a longer compromise. We document each confirmed hop from initial access through lateral movement and privilege escalation, so your team can break the path at the right points.

External perimeter and internal lateral movement
Each hop labelled with the technique used
The full blast radius from a single weak point
host attack path
01
internet
untrusted entry point
entry
exposed service reachable
02
vpn-gw
forgotten service on the perimeter
High
default credentials accepted
03
jump-01
foothold on the jump host
High
lateral movement, creds harvested
04
fileserver
cached domain credentials
Medium
privilege escalation
★
dc-01, DOMAIN ADMIN
full control of the directory
Critical
What we look for

Where the perimeter gives

A representative sample of the dozens of checks we run against PTES and MITRE ATT&CK, spanning exposed services, misconfiguration, missing patches, lateral movement, and Active Directory paths.

Exposed and forgotten internet-facing services

the staging box, old VPN, or admin panel nobody remembers leaving open.

Misconfigurations and default credentials

shipped defaults, weak service settings, credentials never rotated.

Missing patches on reachable hosts

known vulnerabilities on anything an attacker can actually reach.

Lateral movement and privilege escalation

one foothold reused to reach the next host, then domain rights.

Active Directory attack paths

misconfigured trust and permission chains that lead to full domain control.

5 checks
Exposed and forgotten internet-facing services

the staging box, old VPN, or admin panel nobody remembers leaving open.

Misconfigurations and default credentials

shipped defaults, weak service settings, credentials never rotated.

Missing patches on reachable hosts

known vulnerabilities on anything an attacker can actually reach.

Lateral movement and privilege escalation

one foothold reused to reach the next host, then domain rights.

Active Directory attack paths

misconfigured trust and permission chains that lead to full domain control.

How we test

Enumerate the surface, follow the path and map the impact

Step 01

Enumerate the surface

External and internal: we find what is actually reachable.

Step 02

Exploit & pivot

Gain a foothold, then move the way a real intruder would.

Step 03

Map the blast radius

We show how far an attacker gets from a single weak point.

What you get

An attack-path narrative for engineering and leadership

One path from first foothold to full control, so you remediate the whole route.
Penetration Test Report
acme-app / network / engagement summary
01External and internal findingsEverything reachable from outside, and from within.
02An attack-path narrativeThe sequence from the first weak service to the highest confirmed level of access.
03Prioritised remediationFixed in the order that shrinks blast radius fastest.
04Free retesting for one yearAfter you remediate a finding, we rerun the original proof in the tested context and record the result.
The actual report, page by page
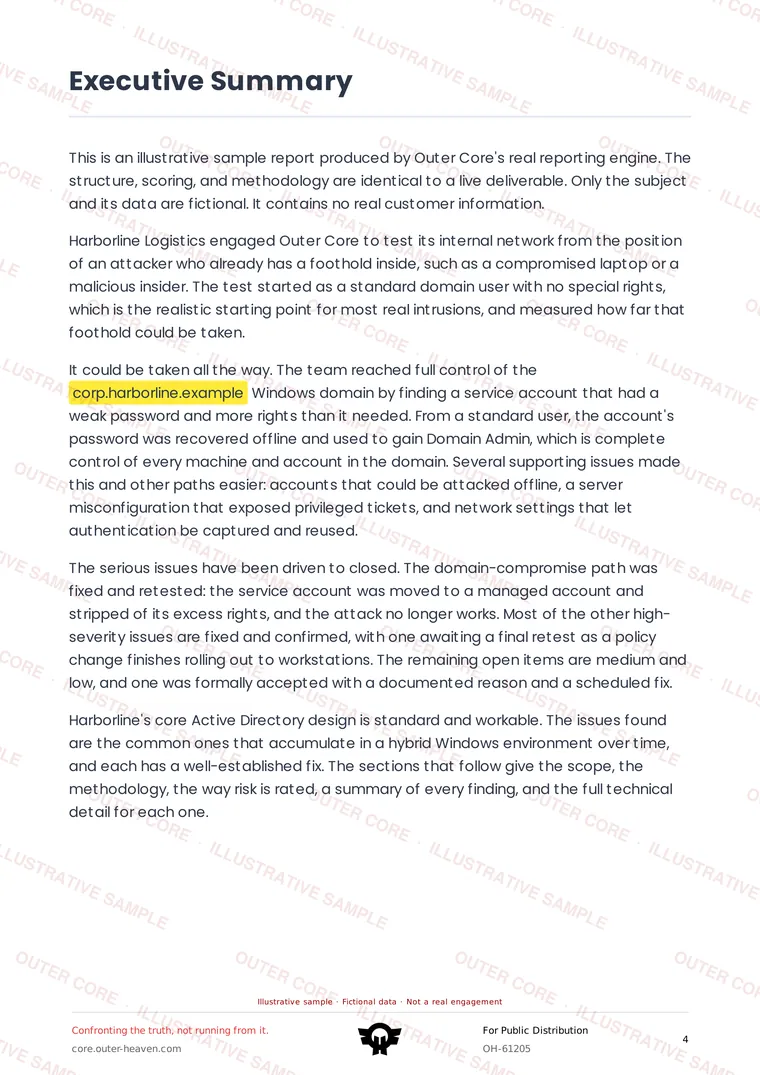
Watermarked sample report page: The report your team receives
01The report your team receives
Watermarked sample report page: Executive summary
02Executive summary
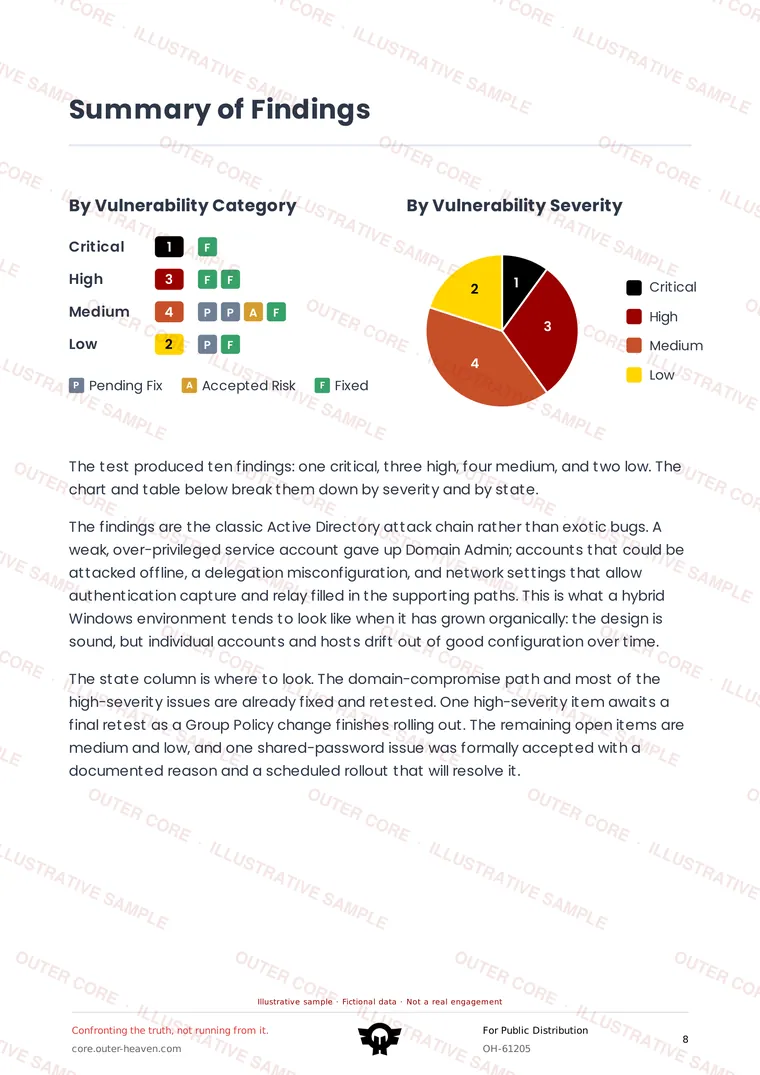
Watermarked sample report page: Findings, ranked by impact
03Findings, ranked by impact
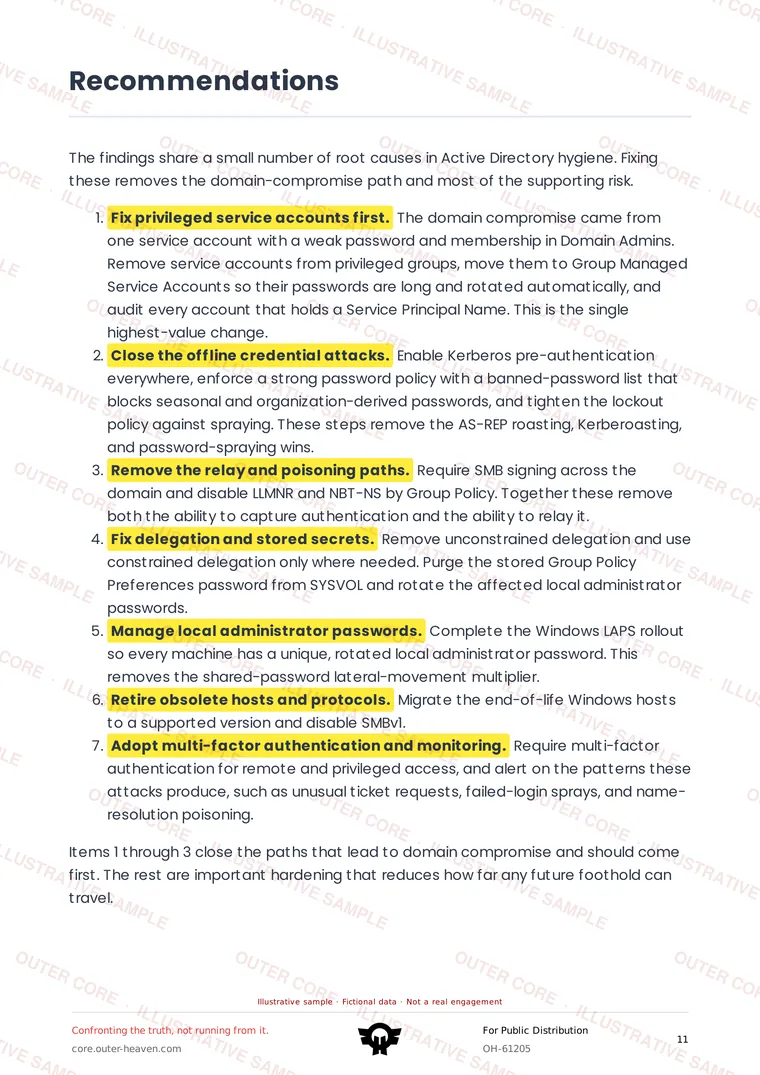
Watermarked sample report page: Recommendations
04Recommendations
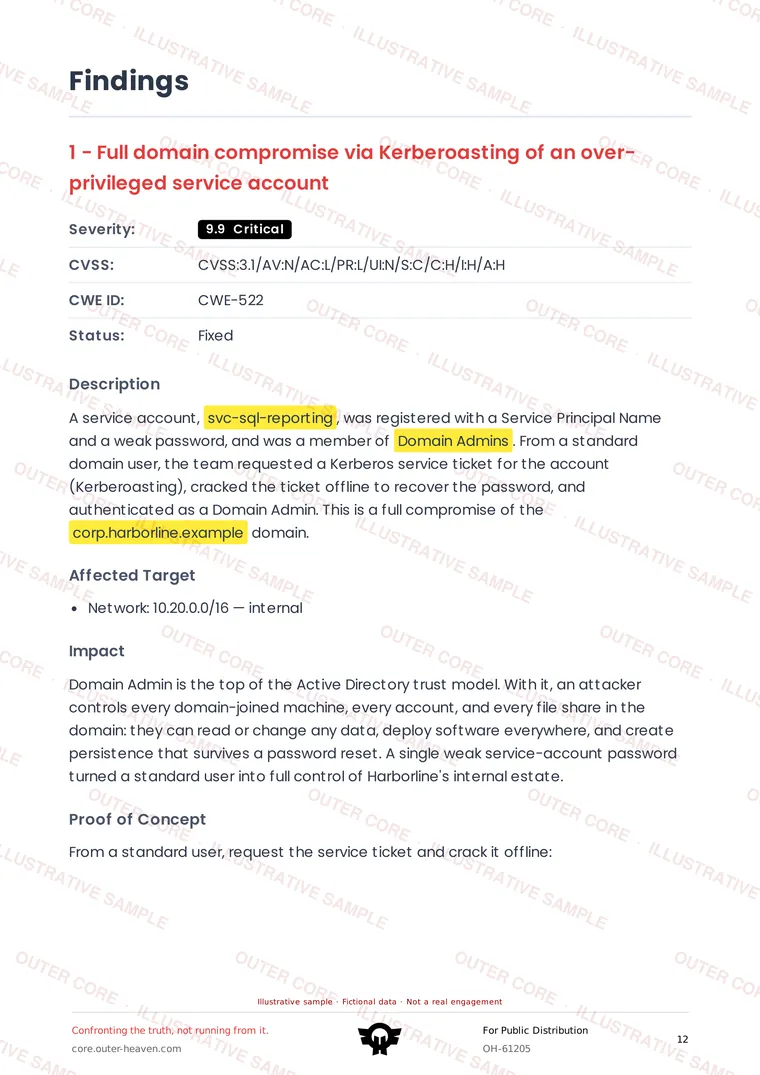
Watermarked sample report page: A finding, reproduced in full
05A finding, reproduced in full
5 sample pages

You're seeing 5 pages. The full report is the complete PDF a customer receives.

As the tester confirms each step, Outer Core records the affected host, technique, evidence and resulting access. Your team can see the developing path, discuss remediation and request a retest.

See how delivery works
Get started

Find the path before an attacker does

Book a scoping call and we'll define the network boundaries, access, depth and testing window together. Confirmed findings and attack paths will appear in Outer Core during the engagement.

Book a scoping call